Podcast Episodes
Back to Search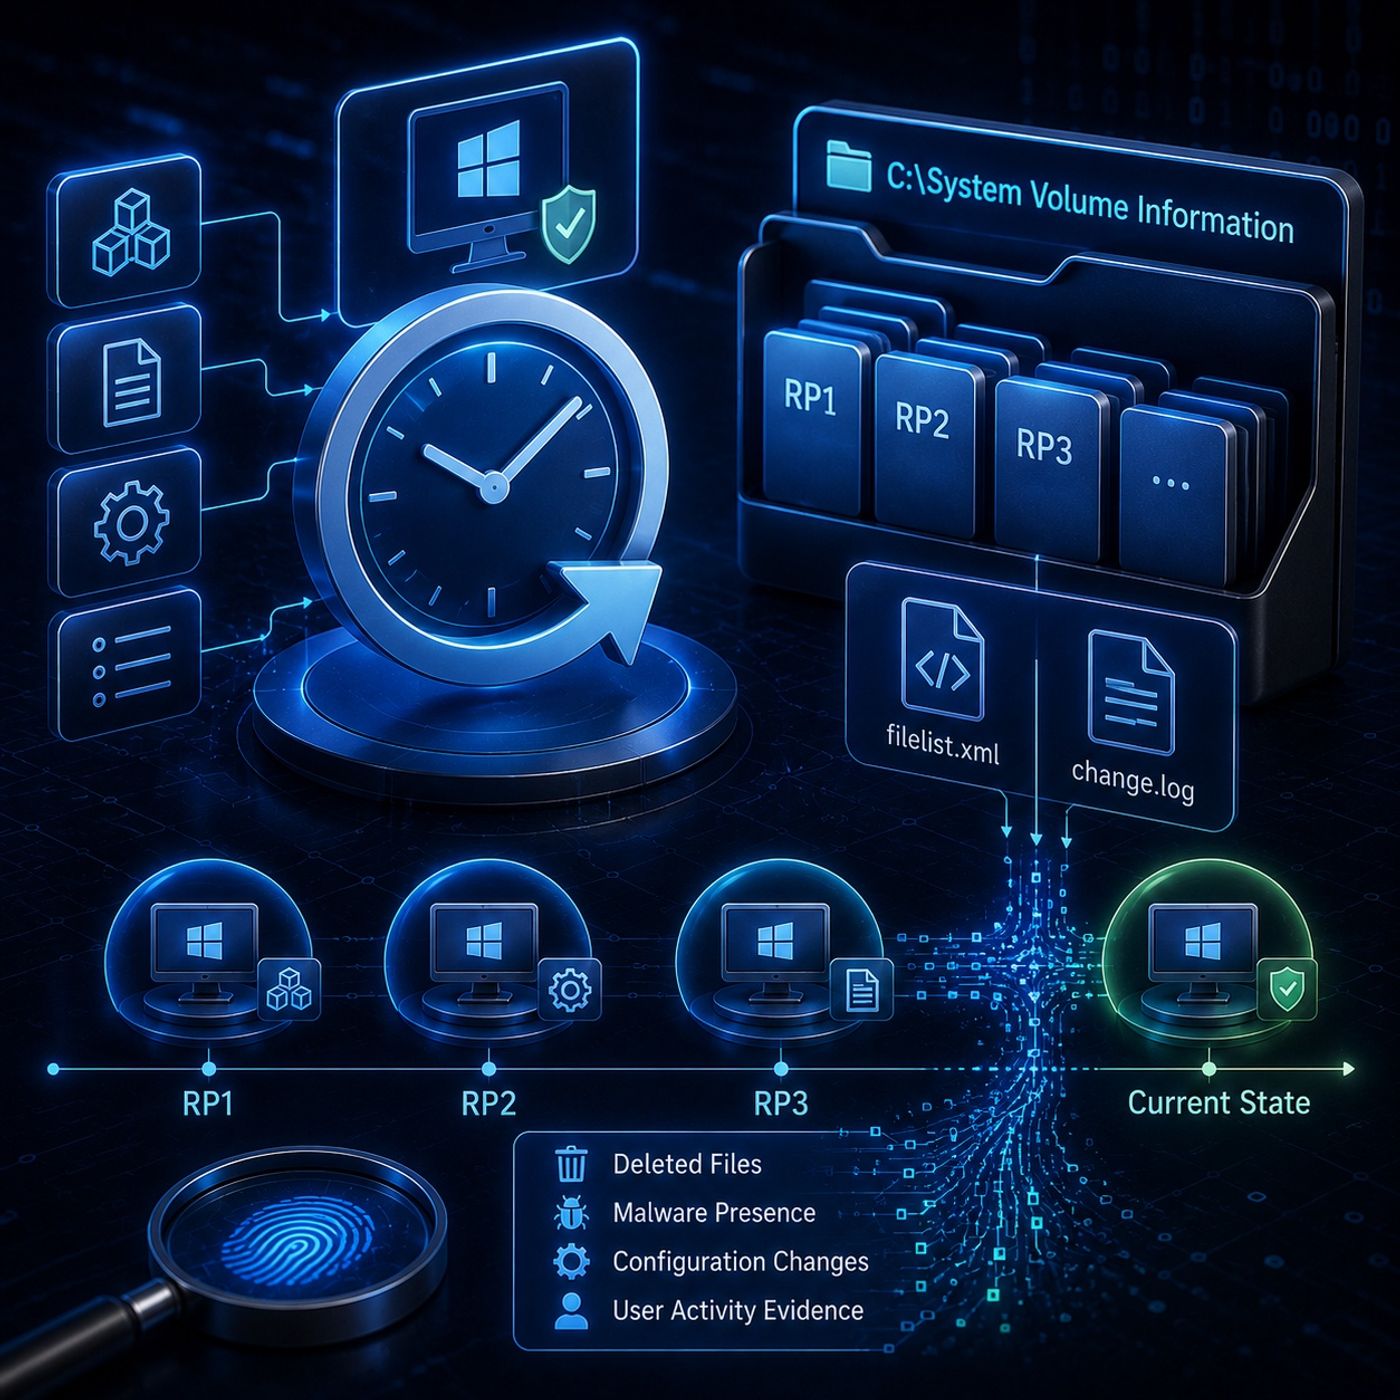
Course 36 - Windows Forensics and Tools | Episode 9: Uncovering Hidden Evidence
In this lesson, you’ll learn about: Windows System Restore Points in digital forensics1. What Are System Restore Points?A Windows feature that create…
4 months, 4 weeks ago
Course 36 - Windows Forensics and Tools | Episode 8: Efficiency, Evidence, and Forensics
In this lesson, you’ll learn about: Windows Prefetch and forensic execution tracking1. What is Windows Prefetch?A Windows performance feature designe…
4 months, 4 weeks ago
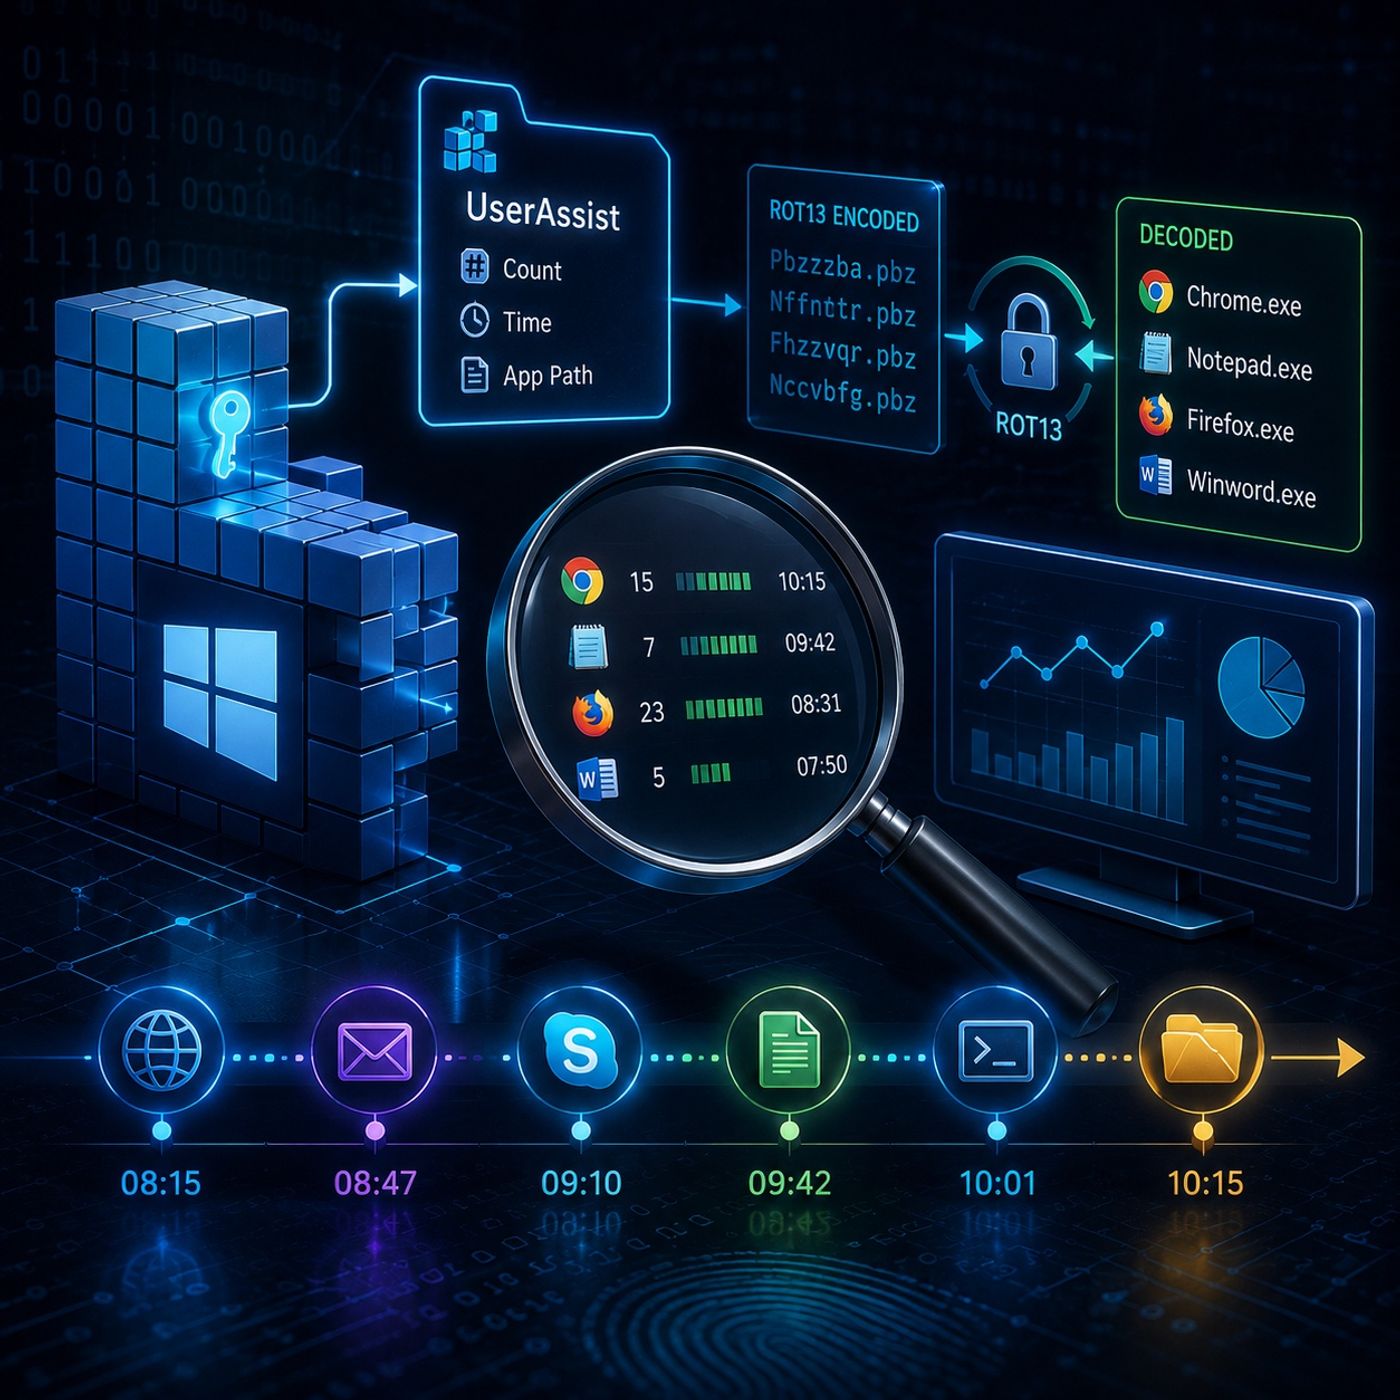
Registry Forensics and the User Assist Key
In this lesson, you’ll learn about: Windows Registry artifacts and UserAssist forensics1. Why Registry Artifacts MatterThe Windows Registry stores hi…
4 months, 4 weeks ago
Course 36 - Windows Forensics and Tools | Episode 6: From System Hives to Forensic Analysis
In this lesson, you’ll learn about: Windows Registry structure and forensic analysis1. What is the Windows Registry?A centralized configuration datab…
5 months ago
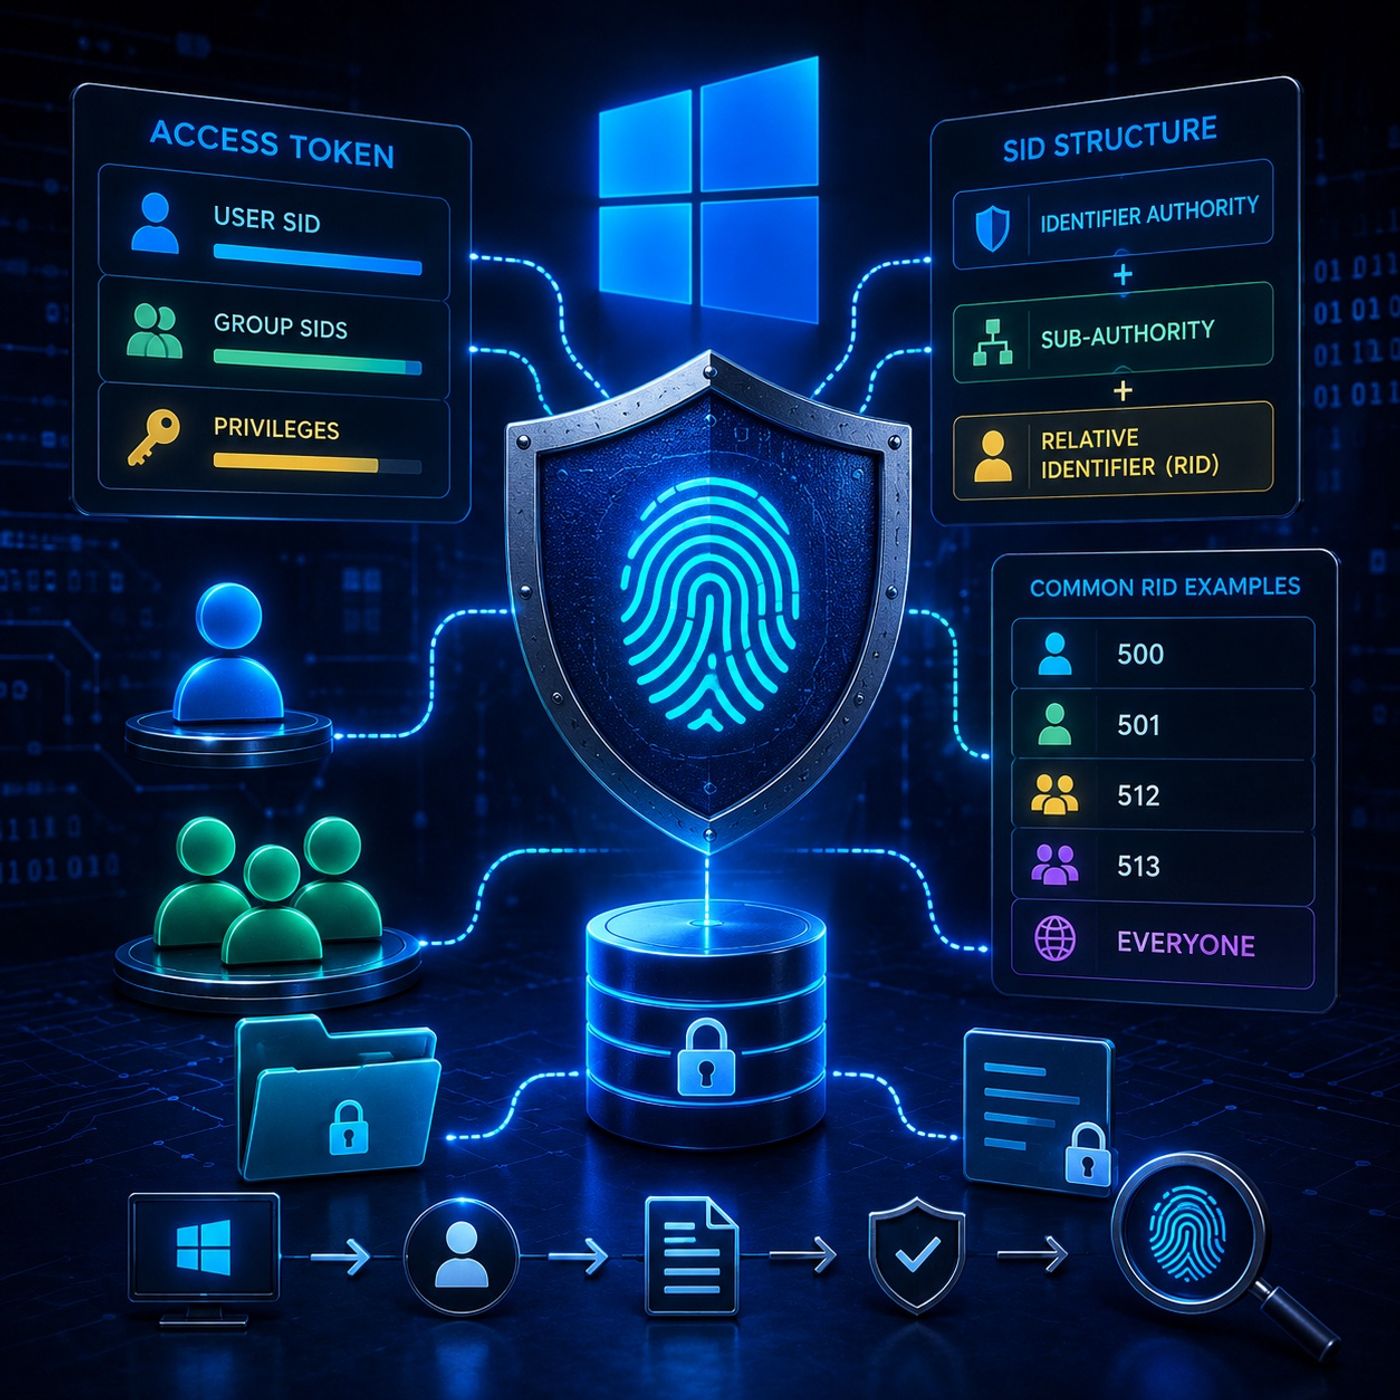
Course 36 - Windows Forensics and Tools | Episode 5: Structure and Forensic Significance
In this lesson, you’ll learn about: Windows Security Identifiers (SIDs) and user tracking1. What is a Security Identifier (SID)?A SID (Security Ident…
5 months ago
Course 36 - Windows Forensics and Tools | Episode 4: From Acquisition to Volatility Analysis
In this lesson, you’ll learn about: memory forensics and RAM analysis1. Why Memory Forensics MattersRAM (volatile memory) is one of the most valuable…
5 months ago
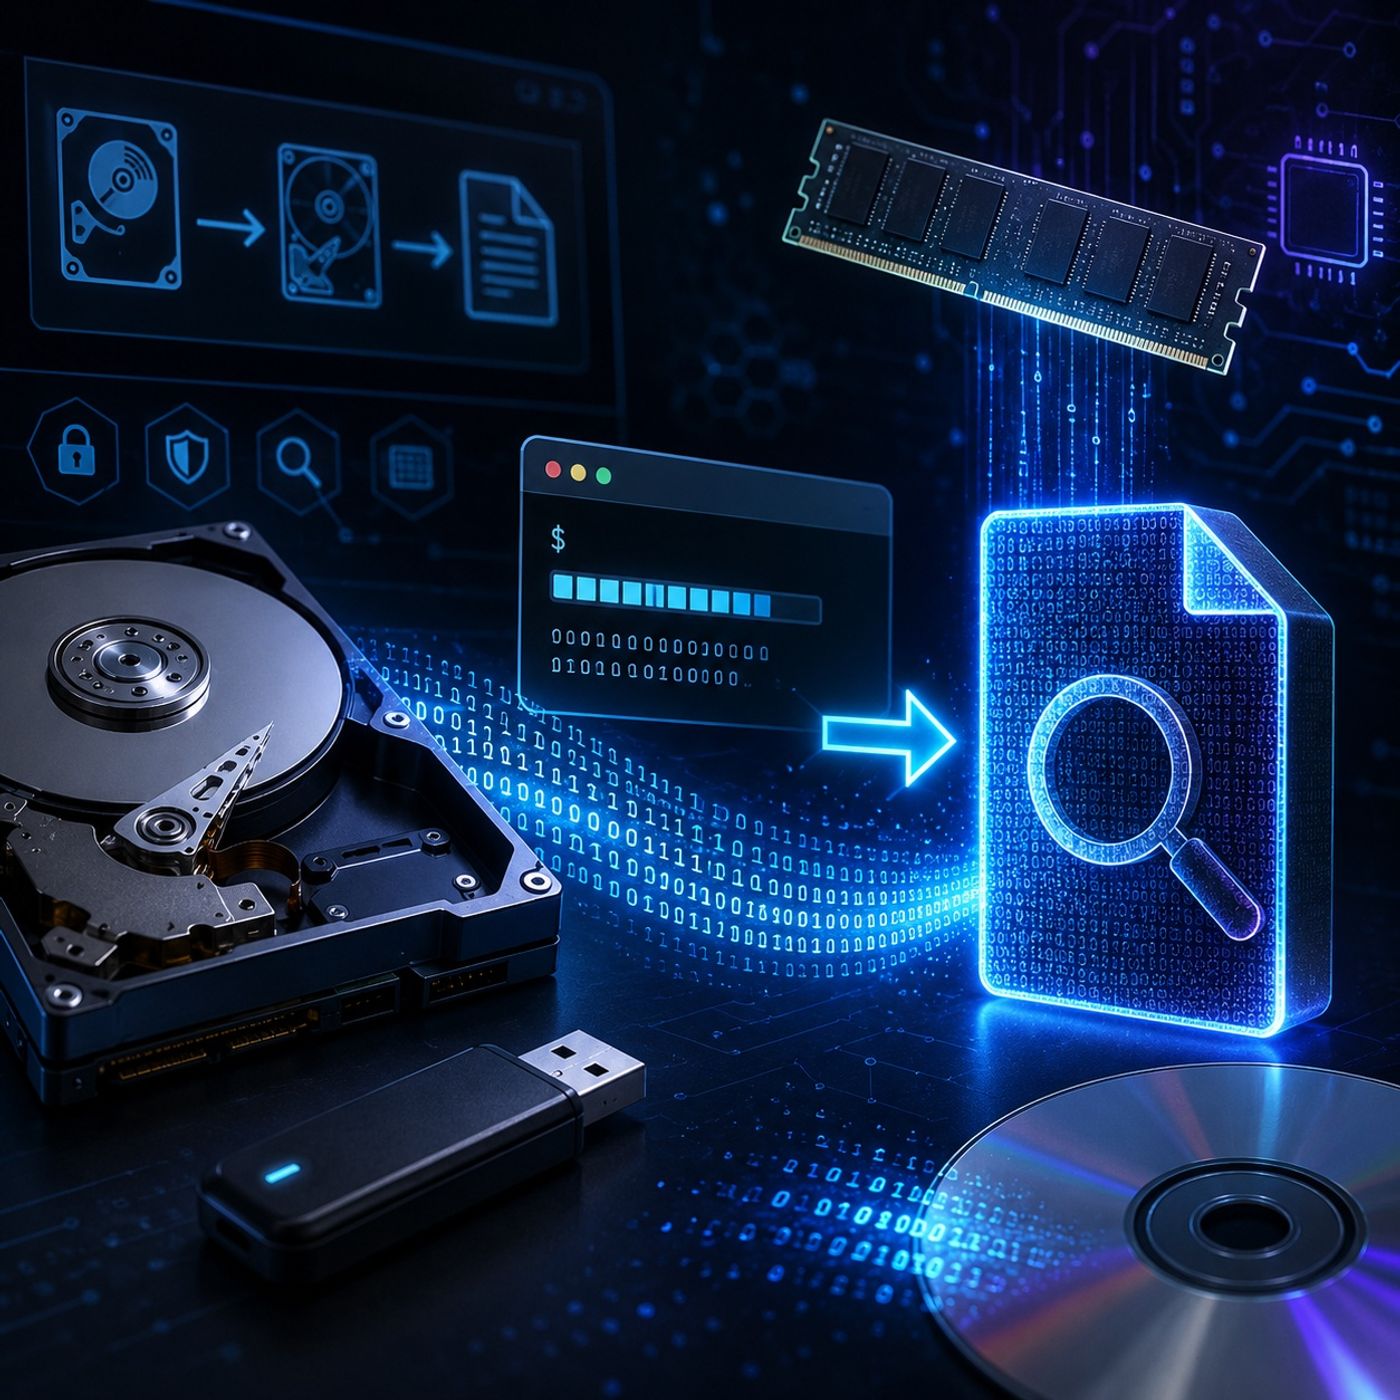
Course 36 - Windows Forensics and Tools | Episode 3: Mastering dd.exe for Drives and Memory
In this lesson, you’ll learn about: forensic imaging using the DD utility1. What is DD (Data Dumper)?A low-level command-line tool used for bit-by-bi…
5 months ago
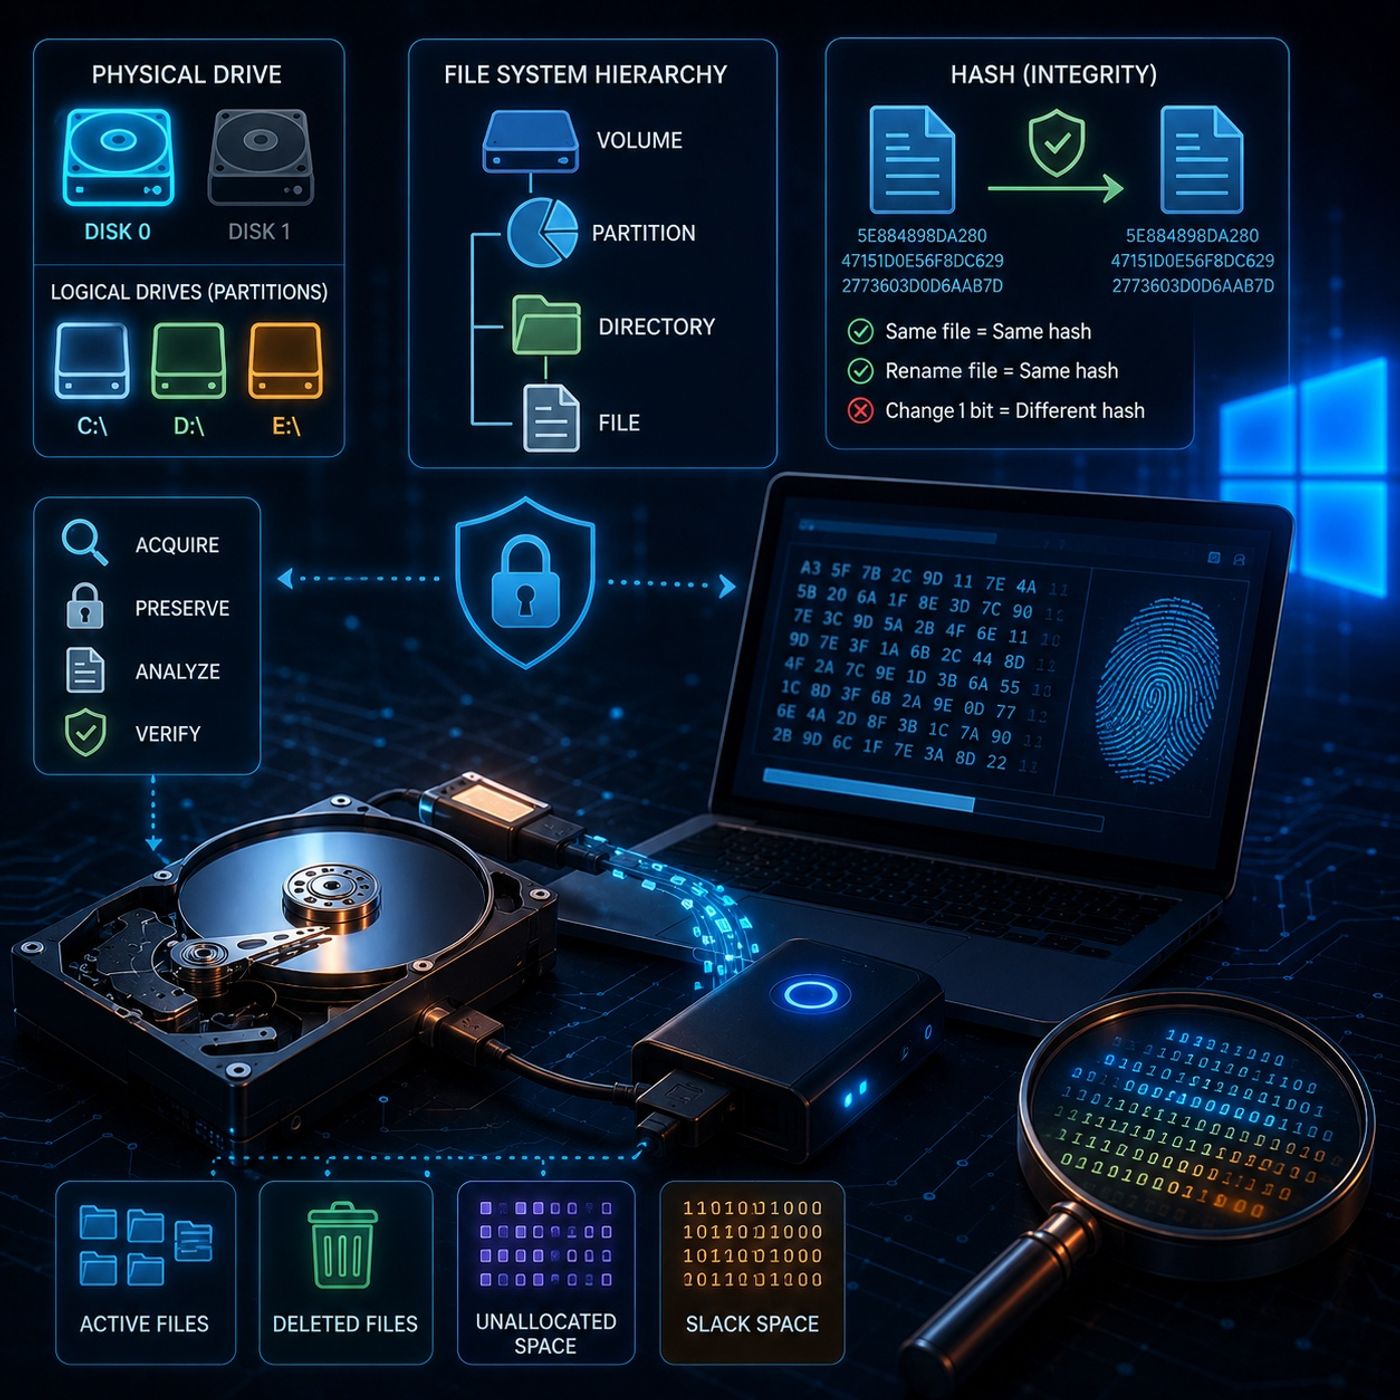
Course 36 - Windows Forensics and Tools | Episode 2: Windows Forensic Imaging and Drive Nomenclature
In this lesson, you’ll learn about: Windows forensic imaging and data structure fundamentals1. What is Forensic Imaging?A bit-by-bit, sector-by-secto…
5 months ago
Course 36 - Windows Forensics and Tools | Episode 1: Debunking Myths and Mastering Methodology
In this lesson, you’ll learn about: digital forensics in Windows environments1. What is Digital Forensics?Also known as computer forensicsThe applica…
5 months ago
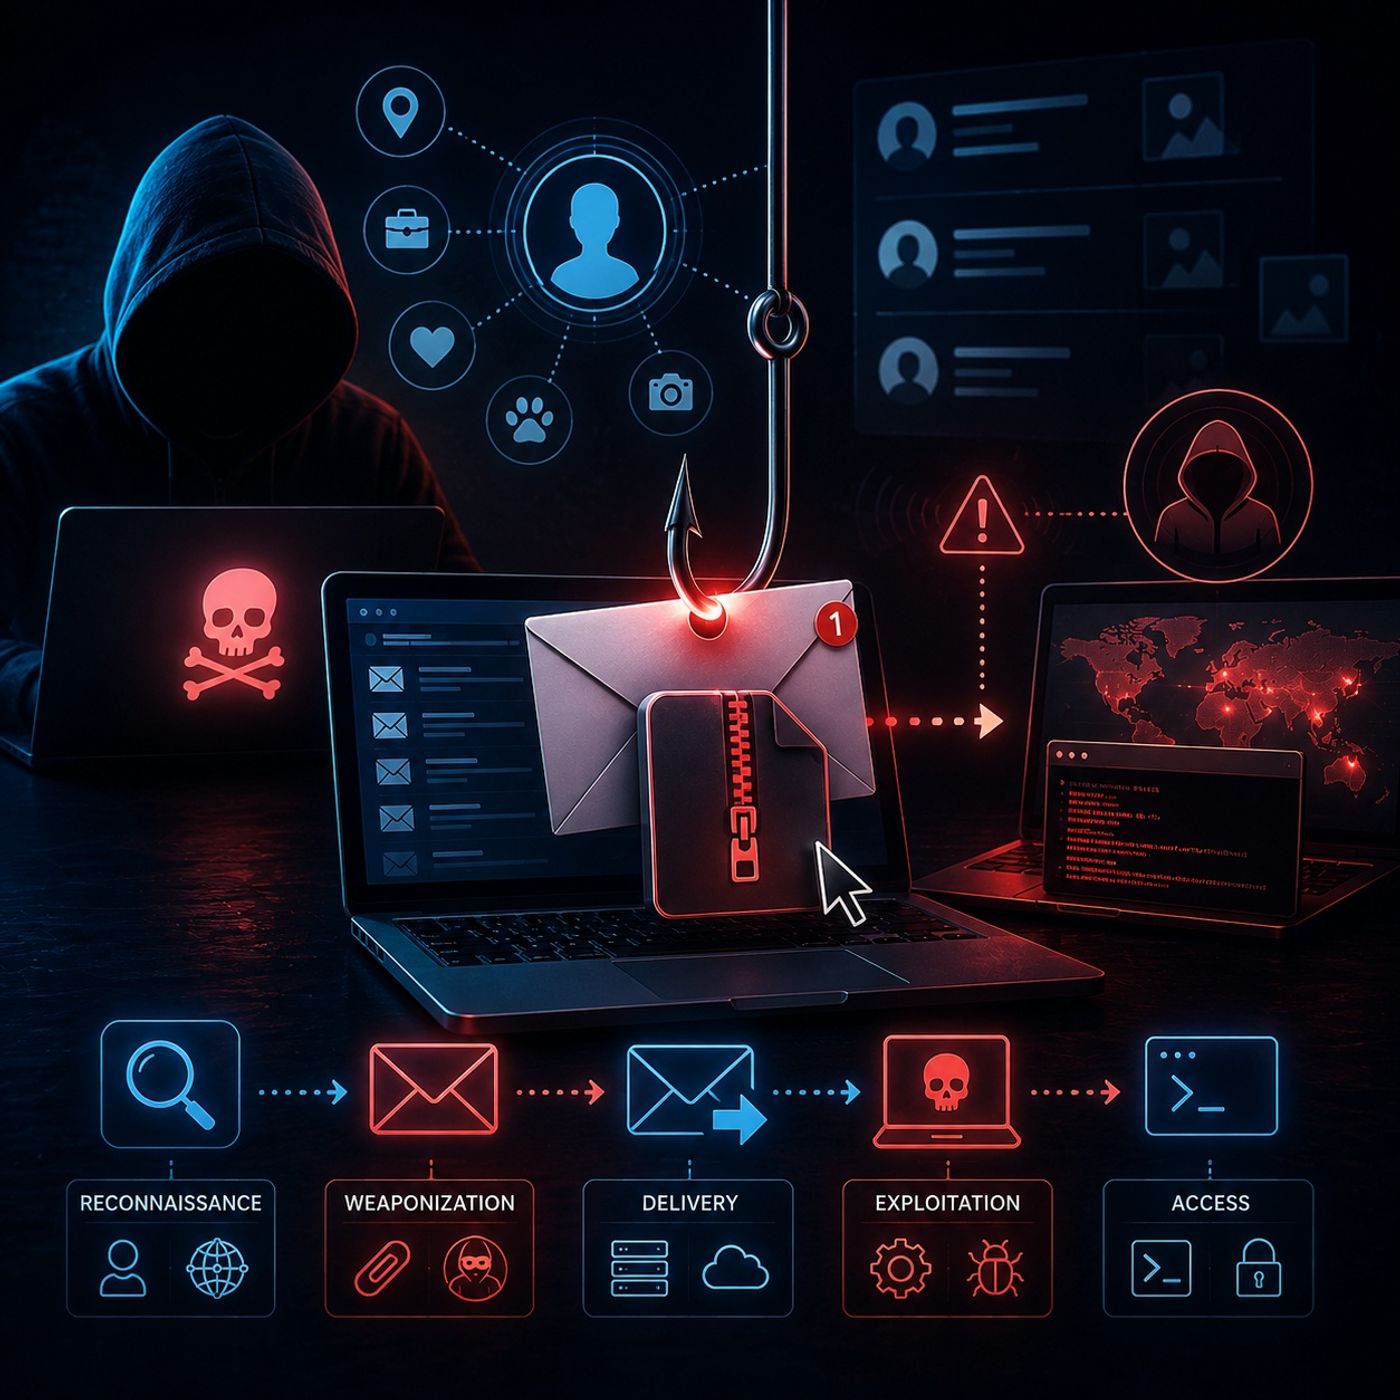
Course 35 - Footprinting and Reconnaissance | Episode 8: From Target Reconnaissance to Phishing Execution
In this lesson, you’ll learn about: social engineering attacks and spear-phishing execution1. What is Social Engineering?A psychological attack techn…
5 months ago