Podcast Episodes
Back to Search
Course 42 - Mobile Malware Analysis Fundamentals | Episode 5: Fundamentals, App Structure, and Knowledge Review
Android Security & APK Architecture — Advanced Study Template1. Android Security ModelAndroid security is built around several fundamental objectives…
1 month, 4 weeks ago
Course 42 - Mobile Malware Analysis Fundamentals | Episode 4: iOS Security and Android Frameworks
A comprehensive technical exploration of the foundational architectures and security models of iOS and Android, providing the essential knowledge req…
1 month, 4 weeks ago
Course 42 - Mobile Malware Analysis Fundamentals | Episode 3: iOS Application Architecture and Jailbreaking Fundamentals
iOS Application Architecture & Jailbreaking — Advanced Study Template1. iOS Application ArchitectureiOS applications are primarily developed using:Sw…
2 months ago
Course 42 - Mobile Malware Analysis Fundamentals | Episode 2: iOS Architecture & Security
iOS Architecture & Security — Study Template1. iOS Architecture OverviewThe iOS platform can be understood as a layered architecture in which higher-…
2 months ago
Course 42 - Mobile Malware Analysis Fundamentals | Episode 1: Threat Landscape, Device Architecture, and Risk Analysis
Mobile Malware Analysis — Foundational Study Template1. Course ObjectiveThis module introduces the fundamentals of mobile malware analysis for both:A…
2 months ago
Course 41 - Analyzing Attacks for Incident Handlers | Episode 4: Live Memory Forensics, VM Troubleshooting, and Malware Analysis
🧠 Live Memory Forensics Lab — Mandiant Redline (Full Workflow)🎯 Lab ObjectivePerform a real-world memory forensic investigation on an infected Window…
2 months ago
Course 41 - Analyzing Attacks for Incident Handlers | Episode 3: Live Memory Forensics and Malware Analysis with Mandiant Redline
🧠 Live Memory Forensics with Mandiant Redline — Study Template🔐 Core ConceptMandiant Redline is not just a memory capture tool — it performs a:Memory…
2 months ago
Course 41 - Analyzing Attacks for Incident Handlers | Episode 2: Utilizing FTK Imager and Redline for Incident Handlers
🧠 Memory Analysis & Incident Response — Advanced Template🔐 Core ConceptMemory analysis is a high-impact forensic technique used during incident respo…
2 months ago
Course 41 - Analyzing Attacks for Incident Handlers | Episode 1: Volatile Evidence, Forensic Tools, and Investigation Procedures
🧠 Memory Analysis (RAM Forensics) — Study Template🔐 Core ConceptMemory analysis is a critical part of the incident response process, used to detect t…
2 months ago
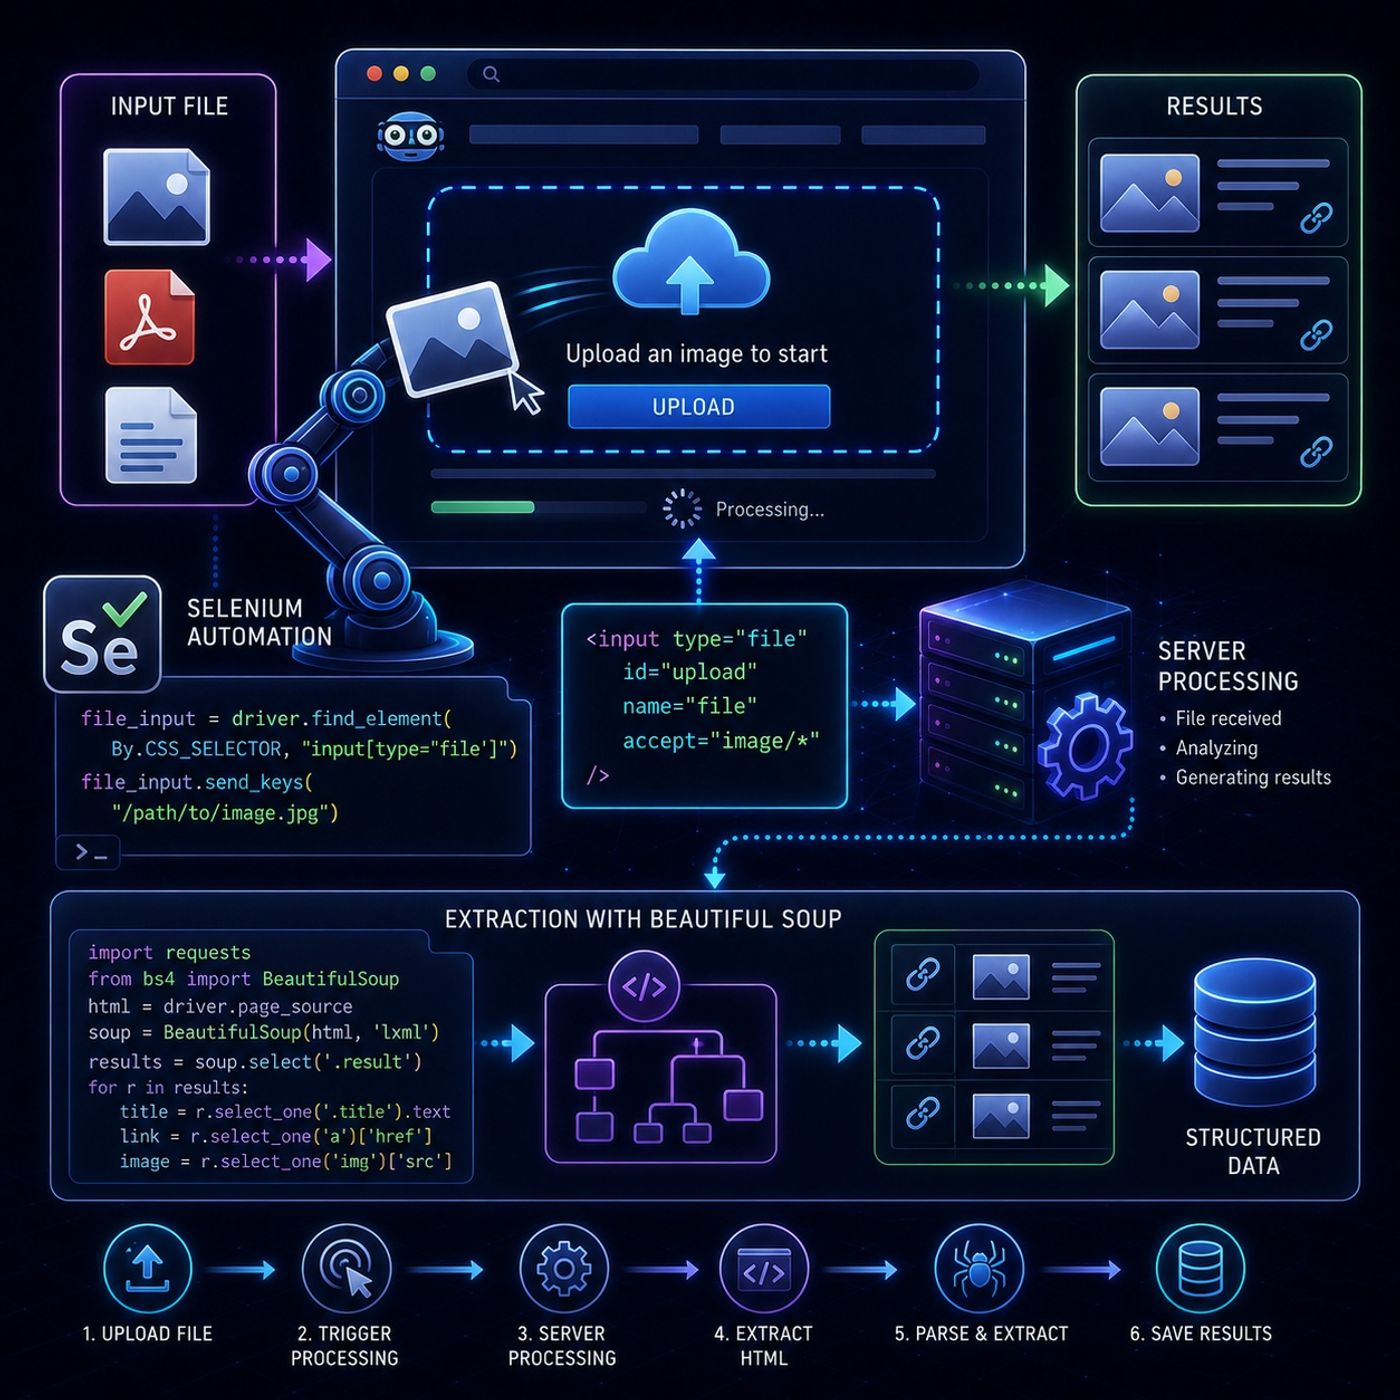
Course 40 - Web Scraping with Python | Episode 43: Mastering File Uploads and Reverse Image Search
This episode is about a very specific but powerful capability in scraping:automating file uploads as part of a web interaction workflowIt sits at the…
2 months, 1 week ago