Episode Details
Back to Episodes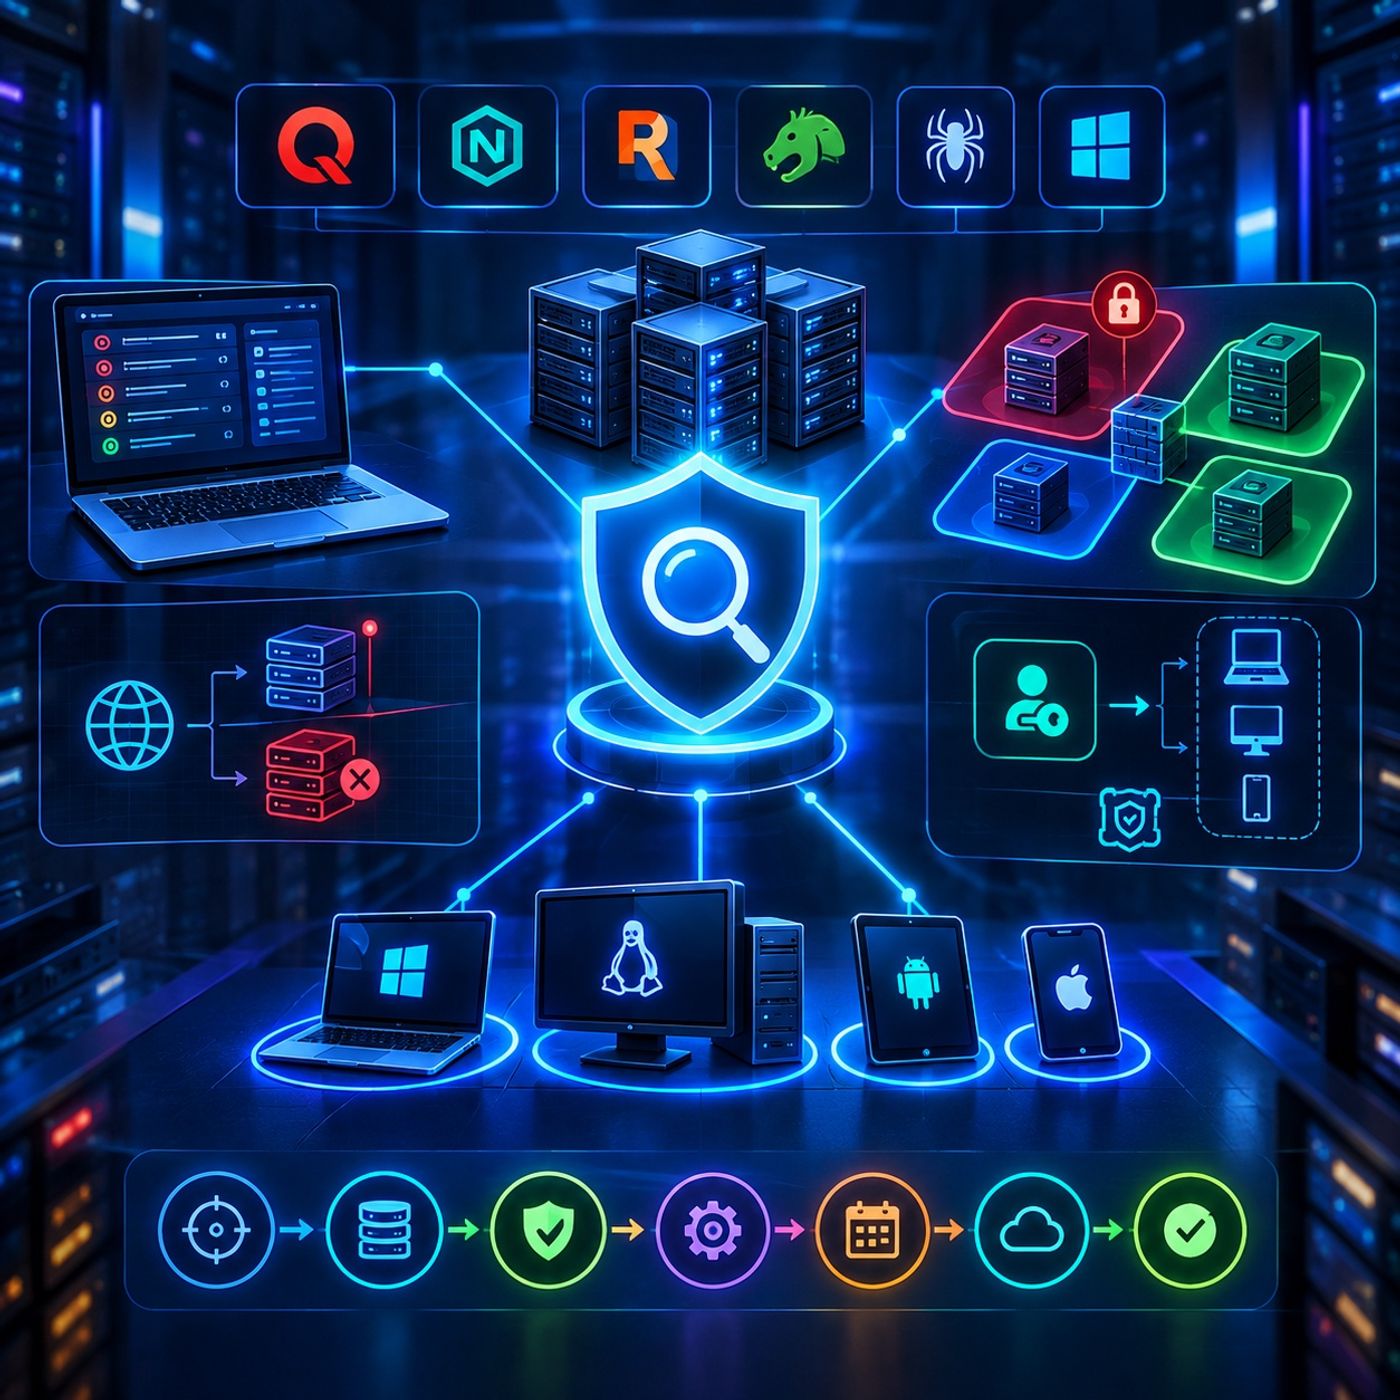
Course 46 - CompTIA Cybersecurity Analyst | Episode 12: Vulnerability Scanning Foundations
Published 1 week, 4 days ago
Description
Episode OverviewThis episode moves from vulnerability management strategy into the practical implementation of enterprise vulnerability scanning. It examines the major scanning platforms used to identify security weaknesses, explains how to establish safe and effective assessment boundaries, and explores the configuration choices that determine the depth and perspective of a vulnerability assessment.The episode also demonstrates how network segmentation can reduce the scope of sensitive environments and simplify compliance efforts while protecting critical systems and data.Key Topics Covered1. Enterprise Vulnerability Scanning ToolsThe episode begins with a comparison of vulnerability-scanning technologies designed for different assessment requirements.Key platforms and tools include:
- QualysGuard / Qualys — enterprise vulnerability management and asset assessment capabilities.
- Tenable Nessus — vulnerability assessment and configuration analysis across a broad range of systems.
- Rapid7 Nexpose — vulnerability management and risk-based assessment capabilities.
- OpenVAS / Greenbone — open-source vulnerability assessment capabilities.
- Nikto — web-server-focused scanning for identifying potentially dangerous files, outdated components, and configuration issues.
- Microsoft Baseline Security Analyzer (MBSA) — a legacy Microsoft tool for assessing certain Windows security and configuration conditions.
- Which networks and hosts should be scanned
- Which systems should be excluded
- What types of checks are permitted
- How scan activity may affect production services
- Which teams and system owners must approve the assessment
- When scanning should take place