Episode Details
Back to Episodes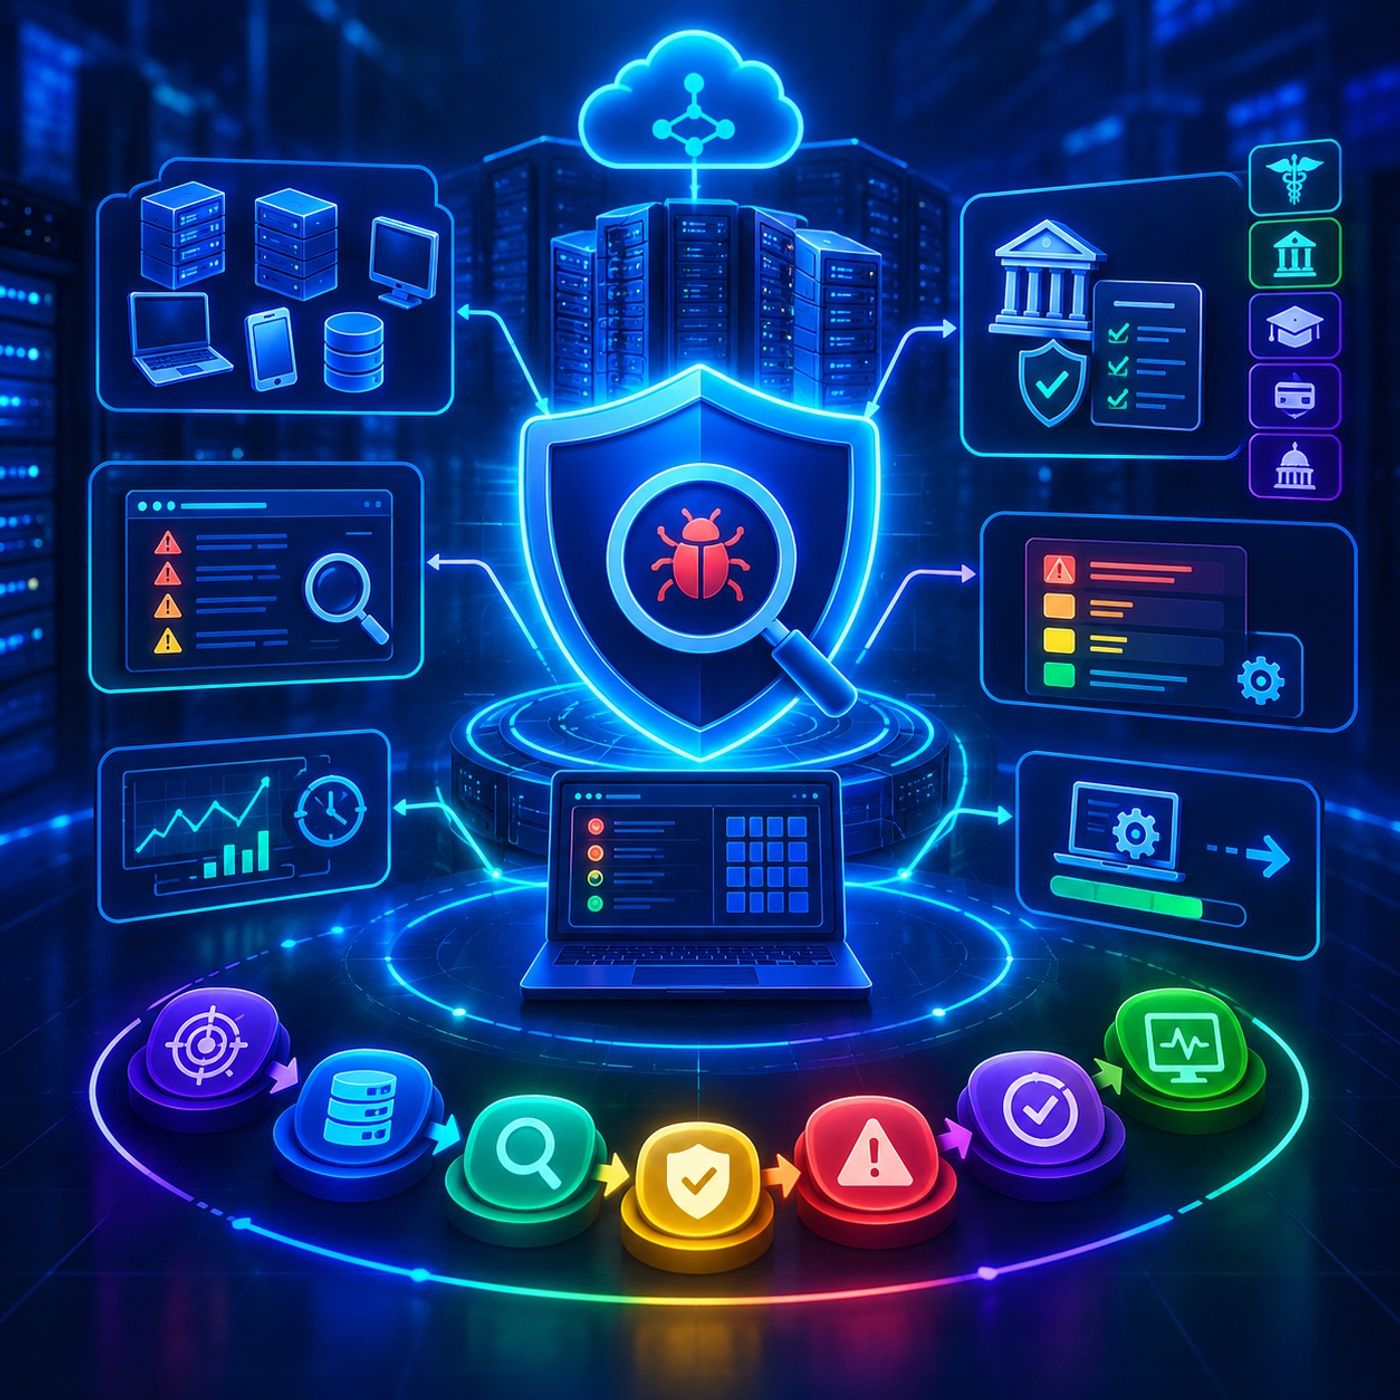
Course 46 - CompTIA Cybersecurity Analyst | Episode 11: Foundations of Vulnerability Management
Published 1 week, 5 days ago
Description
Episode OverviewThis episode explores the end-to-end foundations of a Vulnerability Management Program, moving from the identification of security weaknesses to risk-based prioritization, remediation, governance, and continuous improvement.Rather than treating vulnerability scanning as a one-time technical activity, the episode presents vulnerability management as an ongoing organizational process involving people, technology, policies, compliance requirements, and risk decisions.It examines the regulatory drivers behind vulnerability assessments, the policies required to define an effective scanning program, and the operational challenges organizations face when turning vulnerability findings into measurable security improvements.Key Topics Covered1. Vulnerability Management: Definition and PurposeThe episode begins by defining vulnerability management as the systematic process of:Identify → Assess → Prioritize → Remediate → Verify → MonitorThe objective is to discover security weaknesses before they can be successfully exploited and to ensure that identified vulnerabilities are addressed according to their potential risk.The episode emphasizes that vulnerability management extends beyond running a scanner. A mature program must determine what to scan, how frequently to scan it, how findings should be prioritized, who is responsible for remediation, and how remediation is verified.2. Regulatory and Legal DriversThe episode examines the different types of regulations and standards that influence vulnerability management requirements.It distinguishes general data-protection and privacy regulations from frameworks that contain more explicit requirements around security assessments and vulnerability scanning.Examples discussed include:
- HIPAA — healthcare information security and privacy requirements
- GLBA — financial-sector safeguards and protection of customer information
- FERPA — protection of student education records
- PCI DSS — security requirements applicable to organizations handling payment-card data
- FISMA — federal information-security requirements applicable to U.S. federal agencies and certain related organizations and contractors
- Servers
- Workstations
- Mobile devices
- Network infrastructure
- Internet-facing systems
- Business-critical applications
- Other high-value assets
- Risk appetite
- Asset criticality
- Exposure to external threats
- Regulatory requirements
- Changes to infrastructure
- Newly disclos