Episode Details
Back to Episodes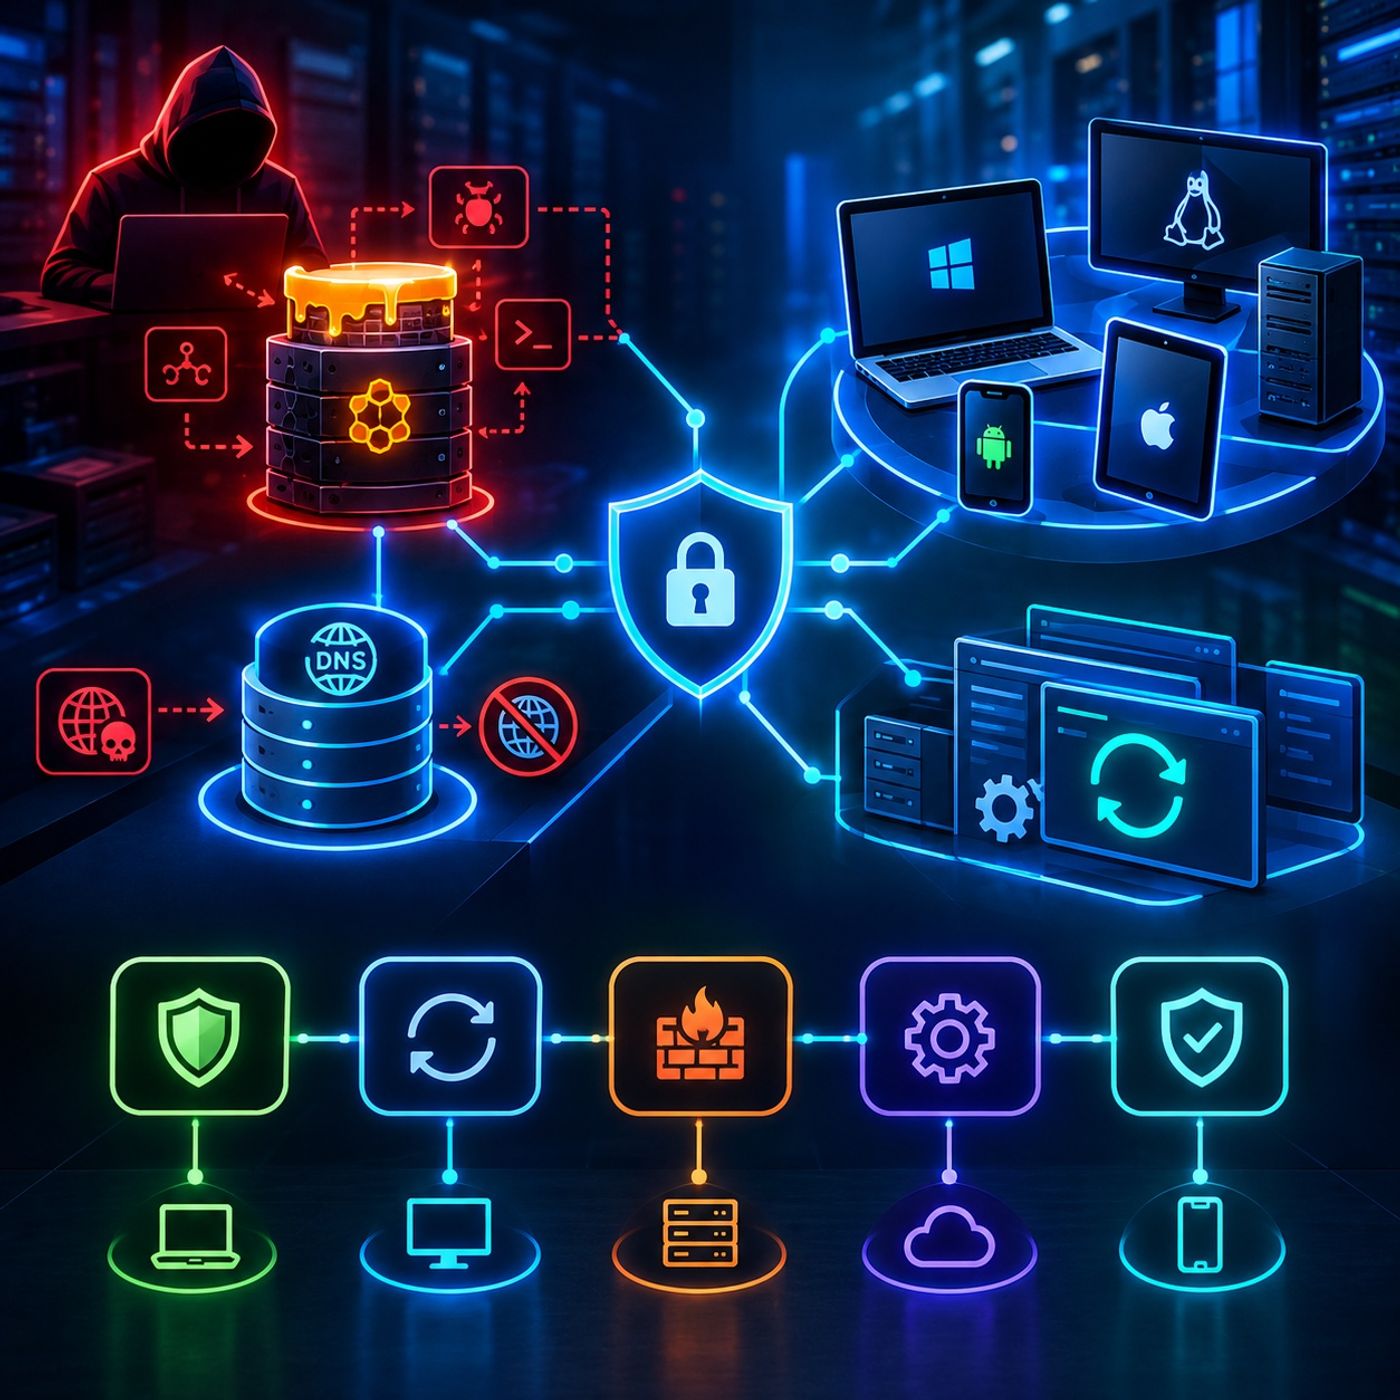
Course 46 - CompTIA Cybersecurity Analyst | Episode 5: Network Deception and Secure Endpoint Management
Published 2 weeks, 3 days ago
Description
Network Defense: Deception, Endpoint Hardening, and Security ManagementEpisode OverviewThis episode expands the network-defense model by examining two complementary areas of cybersecurity: defensive deception and enterprise endpoint security management.The first part introduces deception technologies such as honeypots and DNS sinkholes, showing how defenders can manipulate attacker behavior, collect threat intelligence, and disrupt malicious infrastructure.The second part focuses on protecting the organization's endpoints, including laptops, desktops, and mobile devices. The lesson examines five essential areas of endpoint security:
- System hardening
- Patch management
- Compensating controls
- Centralized configuration management
- Endpoint security software
Together, these techniques demonstrate how modern defense extends beyond the network perimeter and into the individual systems that connect to the organization's environment.Part I: Defensive Deception1. Understanding Defense DeceptionTraditional security controls attempt to prevent, detect, or block malicious activity.Defense deception introduces another strategy:Give the attacker misleading information or controlled targets that can reveal their activity.Instead of simply hiding vulnerable systems, defenders can deliberately create environments that appear interesting to unauthorized users while remaining isolated from legitimate production resources.Deception can provide:
- Early warning.
- Threat intelligence.
- Attacker behavior analysis.
- Malware collection.
- Indicators of compromise.
- Additional detection opportunities.
2. HoneypotsA honeypot is a deliberately deployed system or service designed to attract unauthorized interaction.It may be configured to resemble:
- A vulnerable server.
- A database.
- A network service.
- An exposed application.
- Another potentially valuable target.
The objective is not to support legitimate business operations.Instead, interaction with a honeypot can serve as a security signal.For example:Attacker → Honeypot↓Interaction Detected↓Activity Recorded↓Indicators and Intelligence CollectedThis makes honeypots useful as both detection mechanisms and research platforms.3. Threat Intelligence from HoneypotsOne of the major benefits of a honeypot is the information generated when an unauthorized actor interacts with it.Security teams may be able to observe:
- Source addresses.
- Connection attempts.
- Attack techniques.
- Exploit attempts.
- Malware samples.
- Command sequences.
- Authentication attempts.
- Indicators of compromise.
This information can contribute to broader defensive intelligence.Observed indicators may then be used to improve:
- Firewall rules.
- IDS/IPS signatures.
- Endpoint detection.
- Threat-hunting activities.
- Incident-response procedures.
4. Malware and Attacker Behavior AnalysisA controlled deception environment can also provide a safe location for observing malicious activity.Security researchers can analyze how a malicious program or attacker behaves without exposing a production system to unnecessary risk.A simplified workflow is:Deception System→ Malicious Interaction→ Activity Capture→ Behavior Analysis→ Indicators of Compromise→ Defensive ImprovementsThe isolation and monitoring of such environments are essential because deliberately attracting malicious activity introduces its own security considerations.5. DNS SinkholesA DNS sinkhole provides another form of defensive deception and traffic disruption.Instead of allowing a compromised system to resolve a known malici