Episode Details
Back to Episodes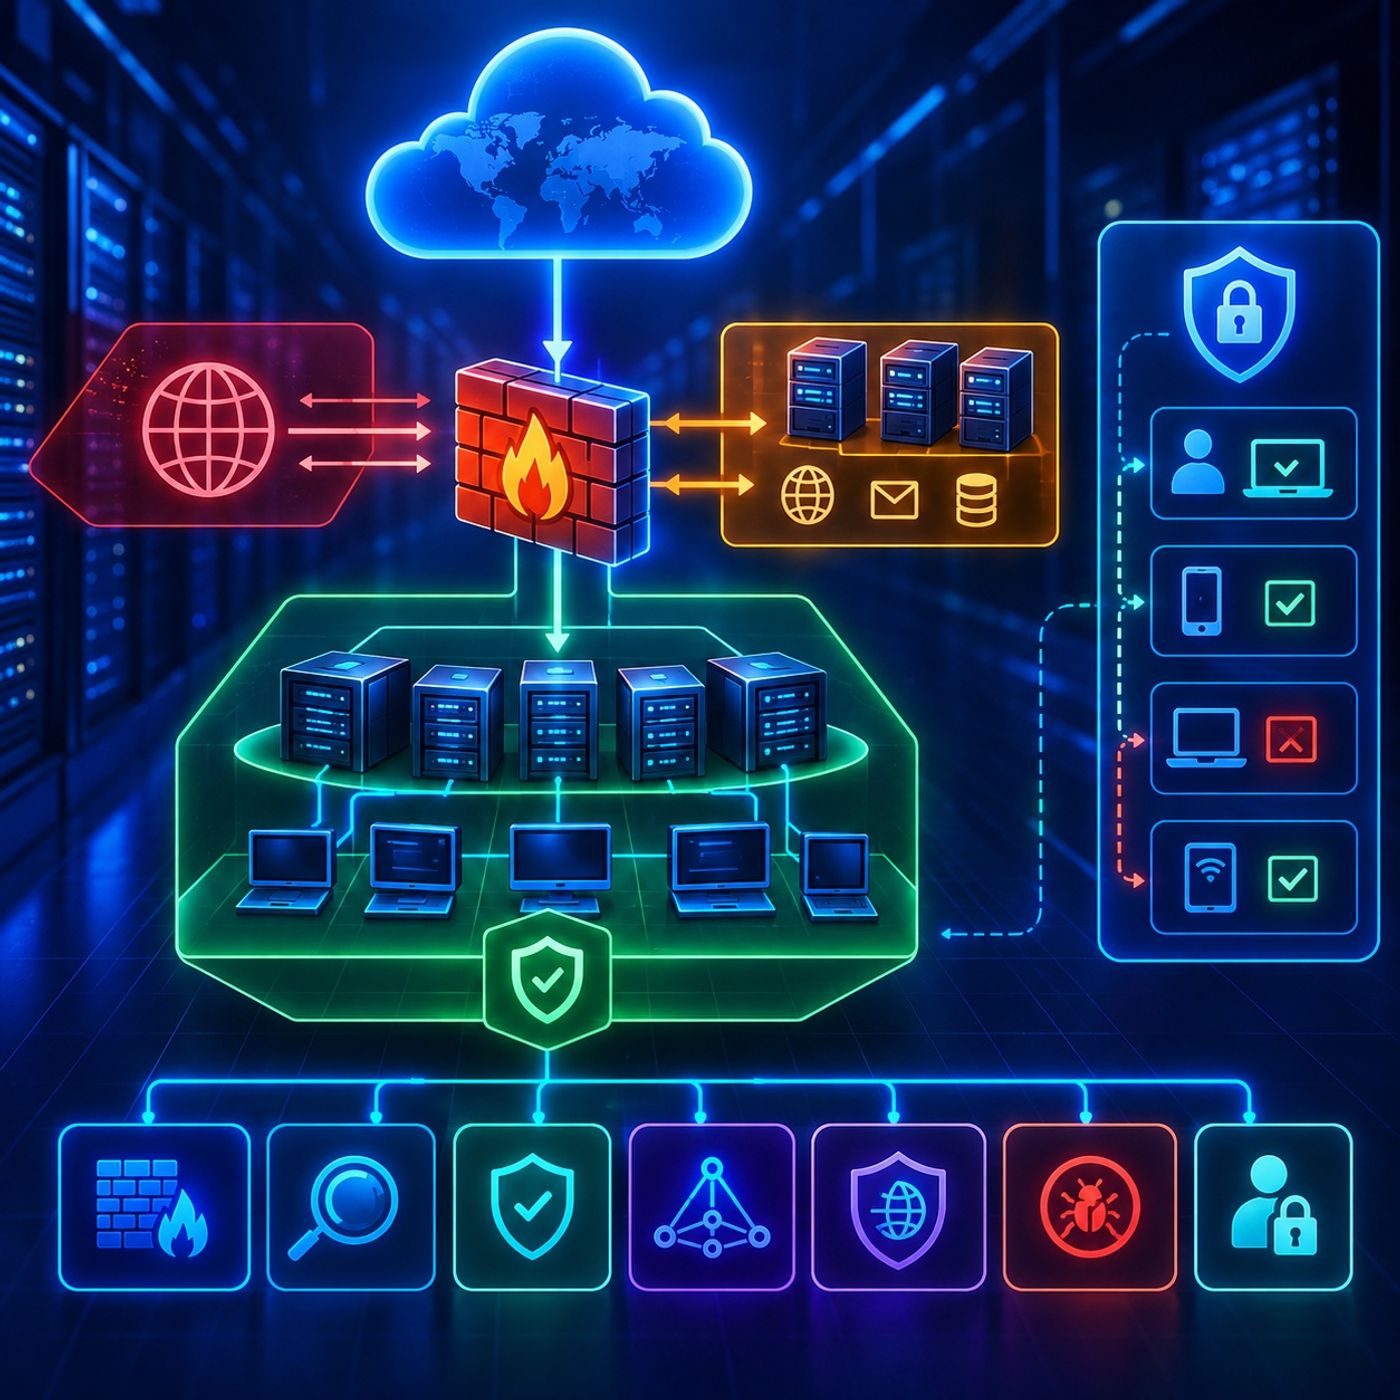
Course 46 - CompTIA Cybersecurity Analyst | Episode 4: Architecture of Isolation: Perimeter Security to Access Control
Published 2 weeks, 4 days ago
Description
Network Defense Fundamentals: Firewalls, DMZ Architecture, and Network Access ControlEpisode OverviewThis episode introduces the core principles of network defense, focusing on perimeter security, network segmentation, traffic filtering, and access management.The lesson begins with the role of firewalls at network boundaries and examines how organizations separate the public internet, internal networks, and semi-trusted environments such as a Demilitarized Zone (DMZ).You will explore firewall architectures, Access Control Lists (ACLs), packet filtering, stateful inspection, next-generation firewalls, and Web Application Firewalls (WAFs). The episode also introduces network port classifications and explains how source addresses, destination addresses, and service ports contribute to traffic-control decisions.The second major topic is Network Access Control (NAC). NAC extends security beyond the network perimeter by evaluating users and devices before granting network access. The lesson examines agent-based and agentless approaches, in-band and out-of-band deployment models, and dynamic access policies based on identity and environmental conditions.Part I: Perimeter Security and Firewall Architecture1. Understanding Network BoundariesA network boundary defines where one level of trust ends and another begins.A typical enterprise environment may contain several distinct security zones:Internet↓Perimeter Firewall↓DMZ↓Internal NetworkEach zone has a different security purpose.The public internet represents an untrusted environment, the internal network contains more trusted organizational resources, and the DMZ provides a controlled location for services that must be accessible from outside.2. The Demilitarized ZoneA Demilitarized Zone (DMZ) is a segmented network designed to host systems that need controlled external exposure.Typical DMZ systems can include:
- Public-facing web servers.
- Reverse proxies.
- Mail gateways.
- DNS services.
- Other externally accessible services.
The purpose is to prevent direct internet access to the internal network.A compromise of a public-facing server should not automatically provide unrestricted access to internal systems.This creates a security boundary between:Internet → DMZ → Internal Network3. Triple-Homed Firewall ArchitectureA firewall can use multiple network interfaces to separate different security zones.A triple-homed architecture can provide connections to:
- Internet
- Internal Intranet
- DMZ
Conceptually: Internet | | [ Perimeter Firewall ] / \ DMZ Internal | Network Public-Facing Services The firewall becomes a central enforcement point between the different trust zones.Traffic between these zones can then be controlled according to explicitly defined security policies.4. Access Control ListsAccess Control Lists (ACLs) define which network traffic is permitted or denied.An ACL can evaluate characteristics such as:
- Source IP address.
- Destination IP address.
- Protocol.
- Source port.
- Destination port.
A simplified rule might conceptually state:Allow → Source A → Destination B → TCP → Port 443while another rule could deny unwanted traffic.The exact syntax and capabilities vary by firewall and network platform.5. Deny by DefaultA fundamental security principle is:Deny by Default → Explicitly Allow Required TrafficInstead of allowing everything and attempting to block known malicious traffic, a restrictive policy permits only the traffic that is required.For example, a public web server may need:
- TCP 443 from the internet.
It may not need:
- Arbitrary inbound administrative services.
- Unnecessary application ports.
- Direct access from untrusted networks to internal databases.
A defau