Episode Details
Back to Episodes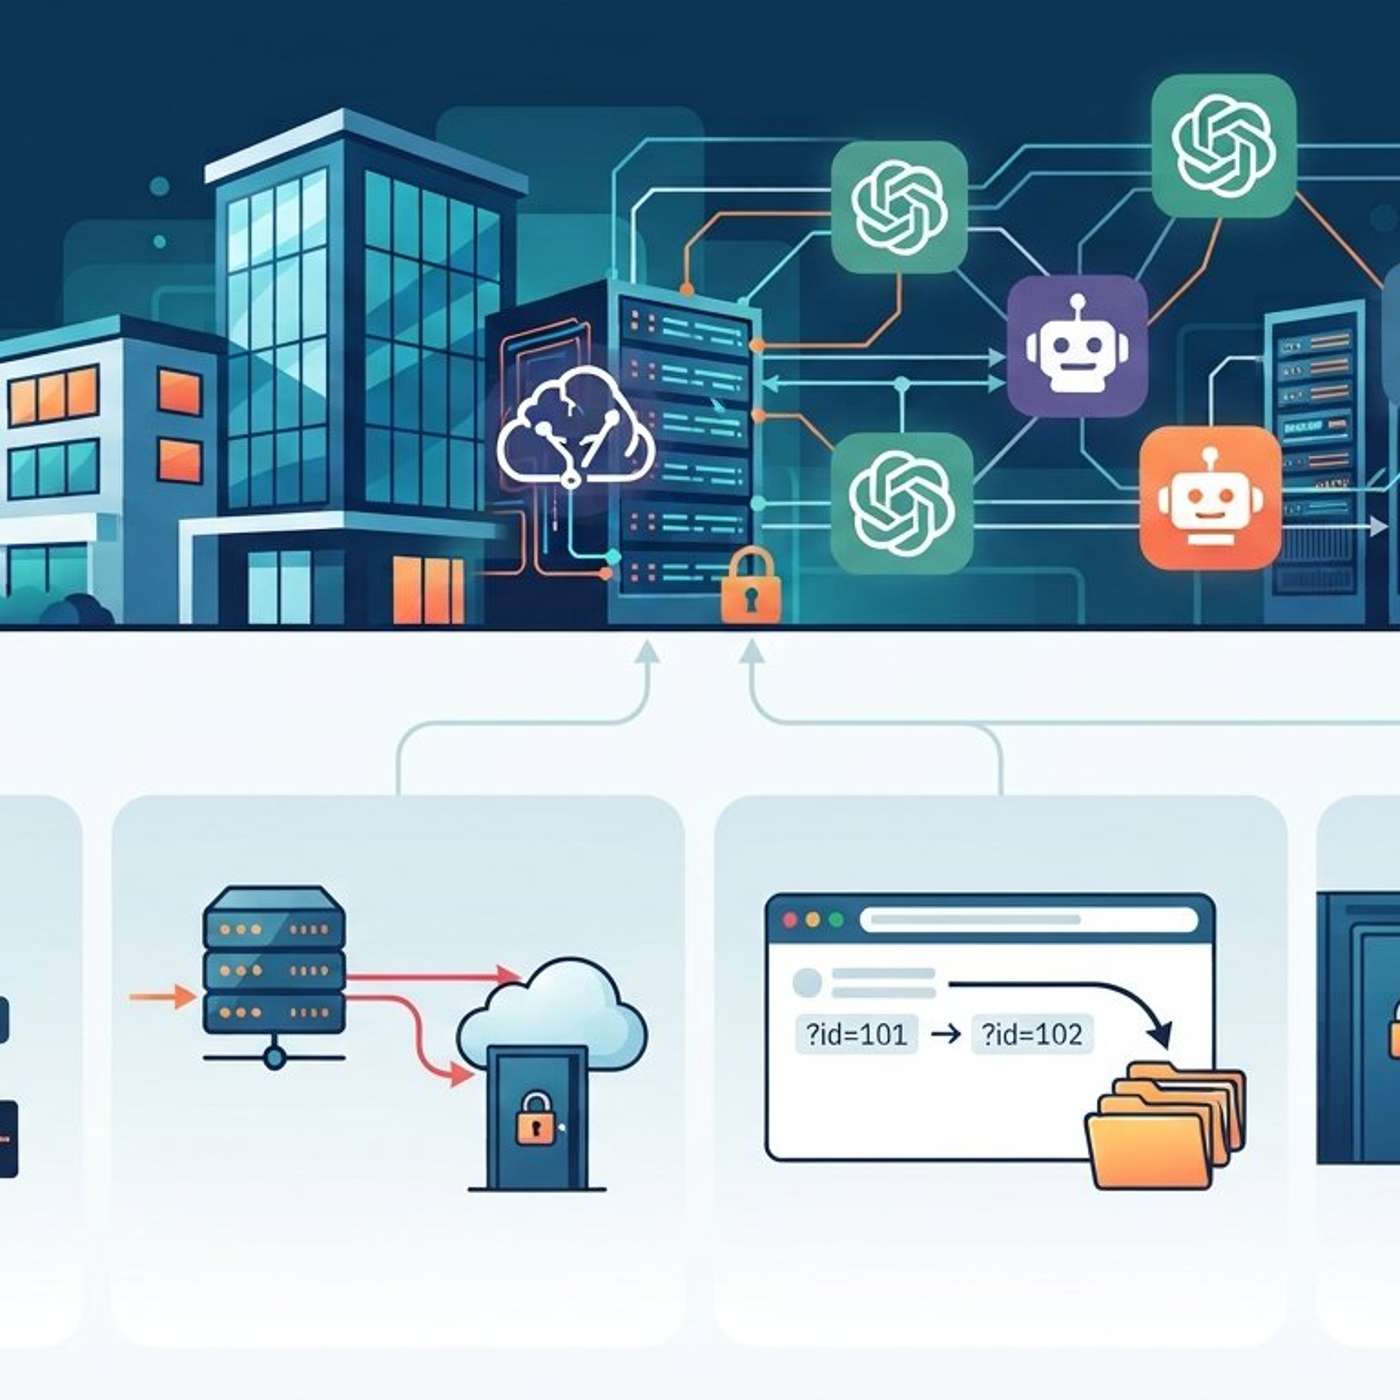
Securing the Open Source AI Ecosystem with Pranshu Raghav
Description
This story was originally published on HackerNoon at: https://hackernoon.com/securing-the-open-source-ai-ecosystem-with-pranshu-raghav.
Open-source AI frameworks are becoming part of enterprise infrastructure. Learn how supply chain flaws, SSRF, IDOR, & weak access controls expand the AI attack.
Check more stories related to undefined at: https://hackernoon.com/c/undefined.
You can also check exclusive content about #open-source-ai-security, #open-source-ai-vulnerabilities, #ai-framework-security, #ai-agent-security-risks, #ai-supply-chain-attacks, #ai-vulnerability-disclosure, #ai-security-architecture, #good-company, and more.
This story was written by: @jonstojanjournalist. Learn more about this writer by checking @jonstojanjournalist's about page,
and for more stories, please visit hackernoon.com.
Open-source AI frameworks are increasingly embedded in enterprise systems, connecting models and agents to internal data, cloud services, authentication systems, and external APIs. That integration expands the security blast radius of vulnerabilities such as agent goal hijacking, SSRF, IDOR, and weak access controls. Cybersecurity engineer Pranshu Raghav explains why AI projects need earlier threat modeling, stronger asset tracking, responsible vulnerability disclosure, and closer collaboration between researchers, maintainers, and enterprise security teams.