Episode Details
Back to Episodes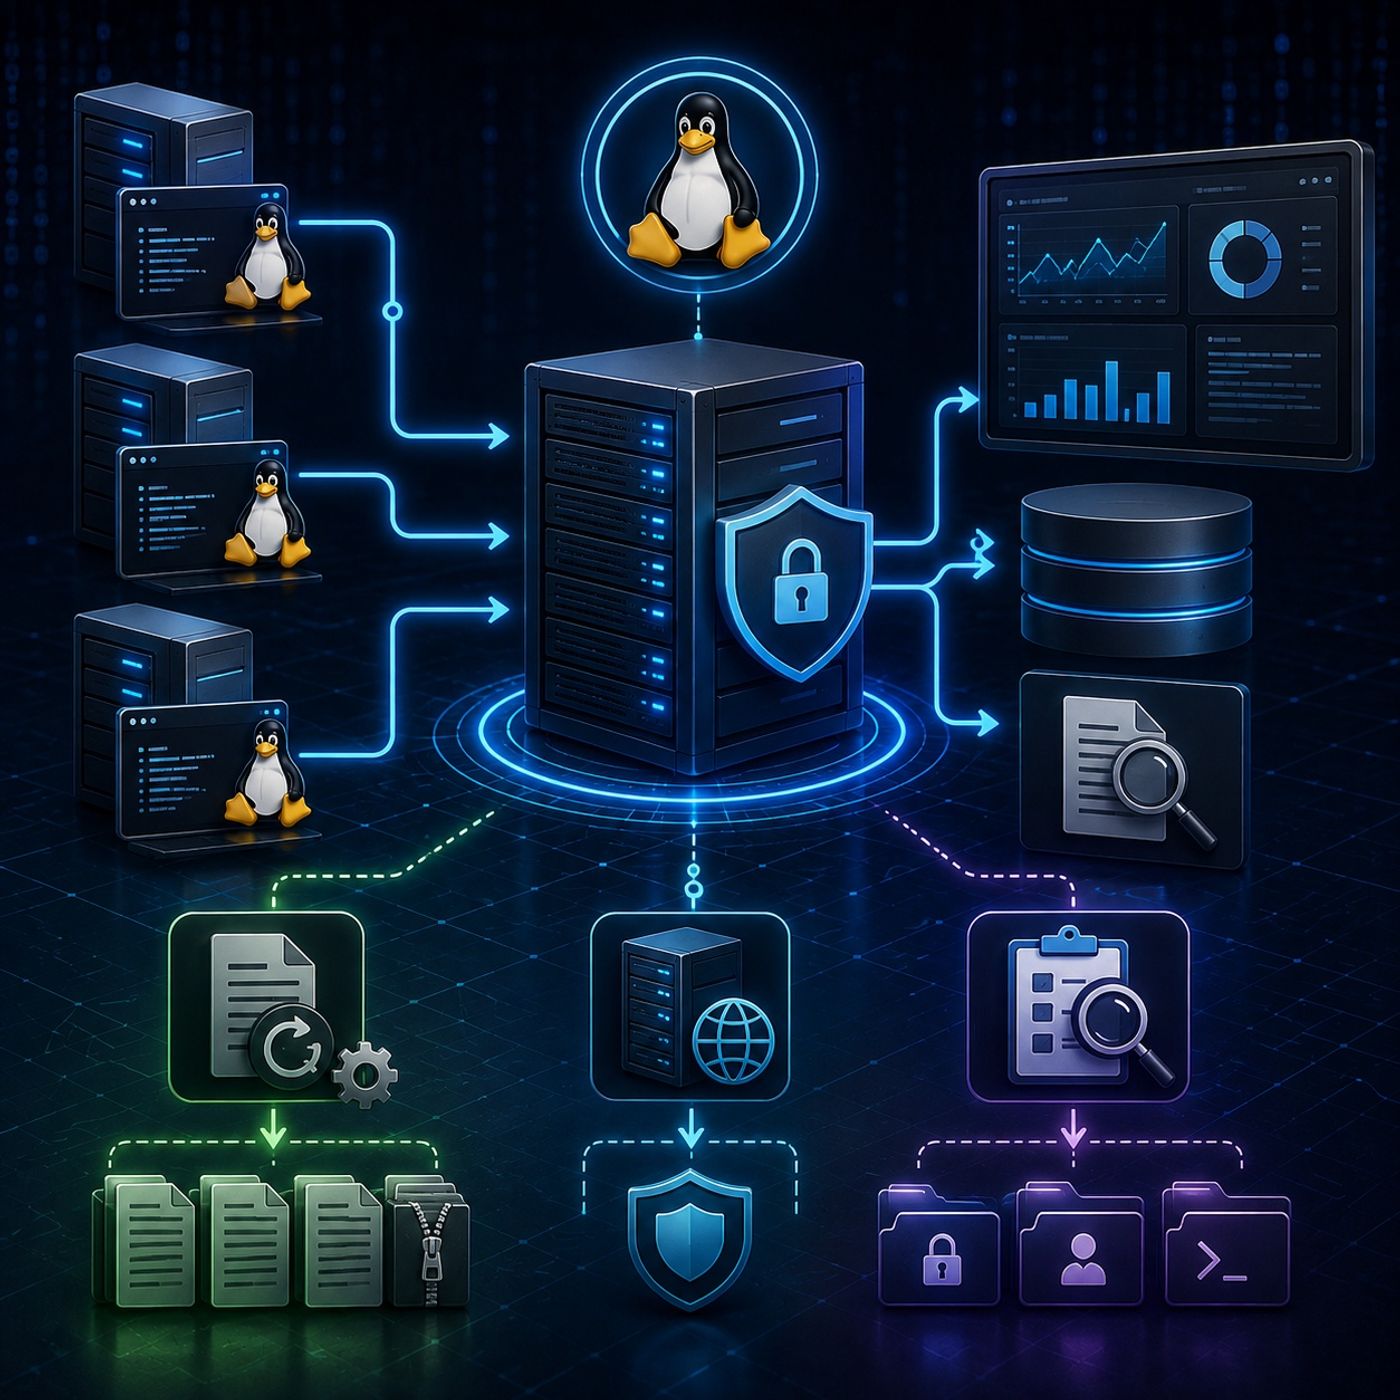
Course 44 - RH Security Specialist | Episode 10: Linux System Logging and Auditing
Published 4 weeks, 1 day ago
Description
A secure Linux environment is only as effective as your ability to understand what is happening inside it.Servers continuously generate information about authentication attempts, system activity, application behavior, administrative actions, and security events. Without proper log management and auditing, this information can become difficult to analyze, consume valuable storage, or disappear entirely when an attacker compromises the system.In this episode, we explore three essential pillars of Linux system visibility and security monitoring: log management, centralized remote logging, and system auditing.You will learn how administrators and cybersecurity professionals manage large volumes of log data, preserve security evidence on centralized systems, and monitor critical operating-system activity through the Linux auditing framework.1. Managing Linux Logs with LogrotateLinux systems can generate enormous amounts of log data over time. If these files are allowed to grow indefinitely, they can eventually consume available disk space and negatively affect system stability.We begin by examining the importance of sustainable log management and introduce logrotate, a utility designed to automate the lifecycle of log files.You will explore how log rotation can:
- Prevent individual log files from growing without limits.
- Create new log files according to a defined schedule.
- Compress older logs to reduce storage requirements.
- Retain historical logs for investigation and troubleshooting.
- Automatically remove logs that have exceeded the configured retention period.
- Log volume.
- Storage capacity.
- Operational requirements.
- Compliance requirements.
- Incident-response needs.
- Retention periods.
- Consolidates events from multiple systems.
- Simplifies monitoring and investigation.
- Reduces dependence on individual machines.
- Helps preserve evidence outside a compromised host.
- Makes it easier to correlate activity across infrastructure.