Episode Details
Back to Episodes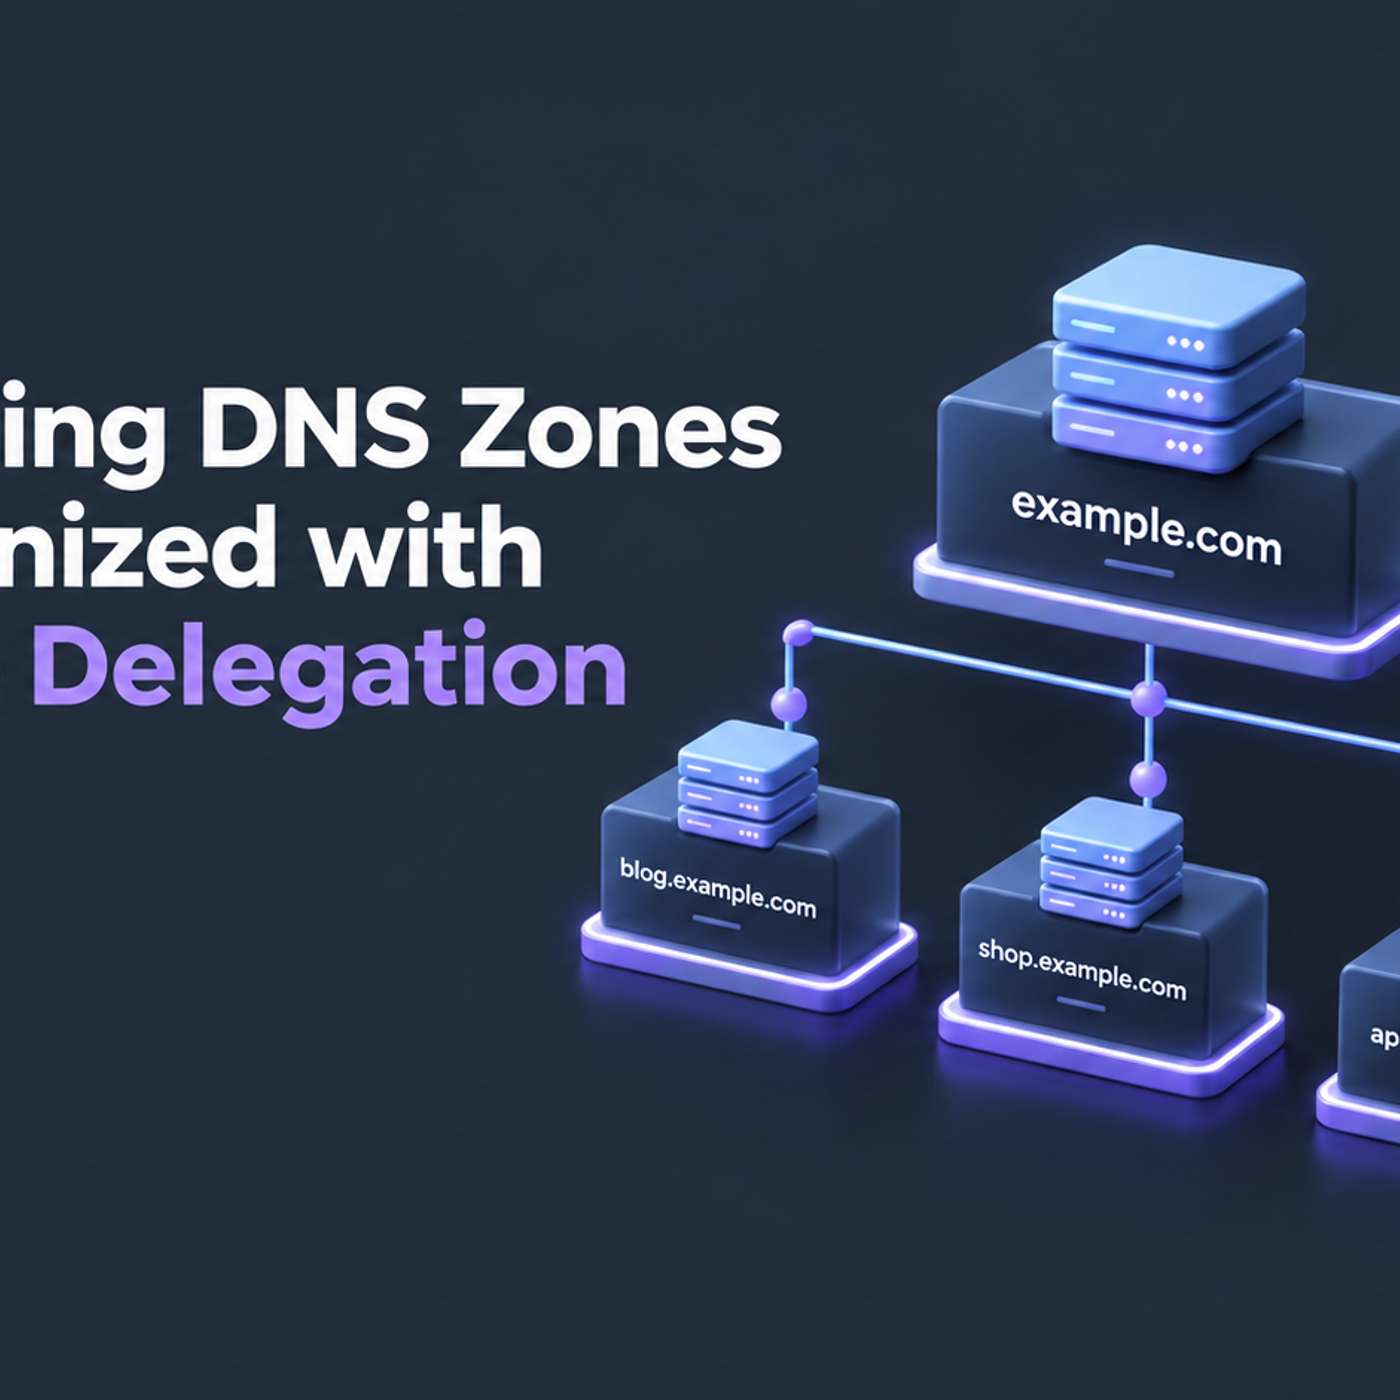
Configuring Route 53 Subdomain Delegation With Terraform
Description
This story was originally published on HackerNoon at: https://hackernoon.com/configuring-route-53-subdomain-delegation-with-terraform.
Delegate environment subdomains to separate Route 53 hosted zones with Terraform, scoped permissions, and DNS verification checks.
Check more stories related to tech-stories at: https://hackernoon.com/c/tech-stories.
You can also check exclusive content about #web-hosting, #amazon-route-53, #dns-delegation, #public-hosted-zones, #subdomain-management, #terraform-aws-provider, #dns-troubleshooting, #infrastructure-as-code, and more.
This story was written by: @lucastonelli. Learn more about this writer by checking @lucastonelli's about page,
and for more stories, please visit hackernoon.com.
Zone delegation is a simple fix to prevent DNS chaos by separating hosted zones for each environment, reducing the blast radius and making IAM more manageable. This is achieved by delegating zones through NS records, allowing each environment to have its own independent zone with isolated record sets.